
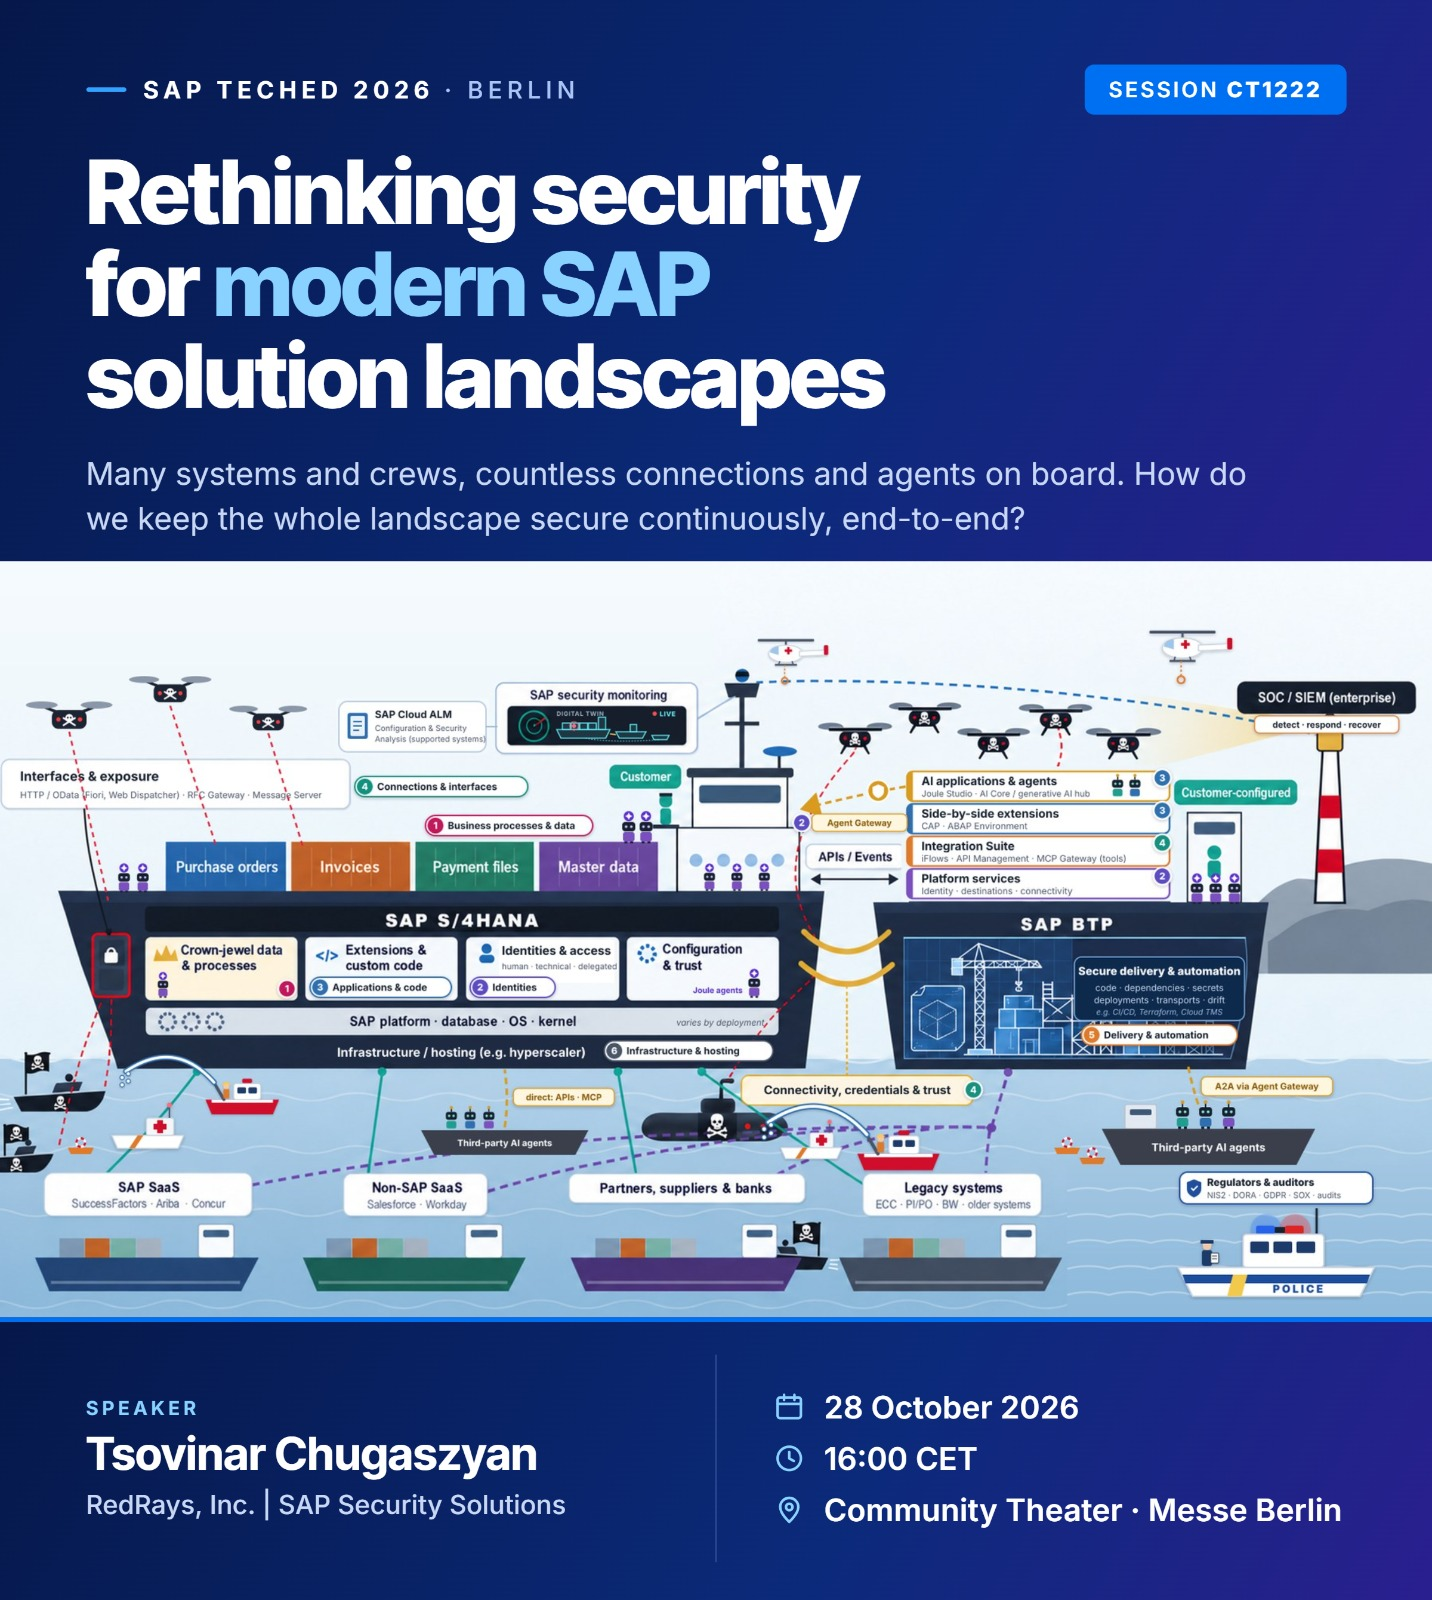
On October 28, Tsovinar Chugaszyan from RedRays will speak at the Community Theater at SAP TechEd Berlin 2026. The session, “Standing watch: keeping a modern SAP landscape safe at sea”, looks at what SAP security means once clean core, SAP BTP, integrations and AI agents are all part of the landscape.
Session details
- Event: SAP TechEd Berlin 2026
- Session: CT1222, Rethinking security for modern SAP solution landscapes
- When: October 28, 2026, 16:00 CET
- Where: Community Theater
- Speaker: Tsovinar Chugaszyan, RedRays
Why this talk
Clean core moves custom logic out of S/4HANA, but the risk moves with it: into BTP extensions, iFlows, pipelines and AI agents. Attackers are getting faster at the same time. SAP and Onapsis reported SAP vulnerabilities weaponized within 72 hours of a patch release, and new unprotected SAP cloud systems compromised in under three hours. In 2025 the NetWeaver Visual Composer flaw (CVE-2025-31324) was exploited before a patch existed. A quarterly review can’t keep up with that pace. The watch has to be continuous: continuous SAP security monitoring across S/4HANA, SAP BTP and everything connected to them, not a yearly snapshot. SAP BTP security, interfaces and AI agents now belong in the same picture as the ERP core.
What we will cover
The talk uses one picture: a ship that never docks, and the crew that keeps watch over it. It walks through six habits that apply to every part of the landscape, from business processes and identities to code, interfaces, delivery pipelines, the platform and AI agents:
- Own it: who owns each system, and what SAP and your providers own
- Know it: a living inventory and an approved baseline
- Scan it: find weak spots in code, settings and access before attackers do
- Fix it: patch by risk, through the pipeline, with tested restore
- Watch it: SAP signals in the SOC, every alert owned, 24/7
- Prove it: evidence produced automatically, not by screenshots
We will also look at where the industry stands. In the SAPinsider 2026 benchmark, 70% of organizations have an SAP incident response plan, but only 38% have tested it, and only 42% know which security tasks sit with SAP. SAP incident response only works if it has been rehearsed with SAP and your providers. You will leave with six questions to take back to your own landscape.
Join the SAP Security Practitioners Taskforce
No single team can work this out alone. We are starting an independent SAP security community for SAP customers, partners, SAP employees, researchers and practitioners who want to build a practical, continuous approach to SAP security together. Expect virtual roundtables, webinars and masterclasses, shared attack stories, and joint work on practical guidance. All experience levels are welcome, whether you want to contribute or just listen and learn.
Can’t make it to SAP TechEd Berlin 2026? You can still join the SAP security community. Fill in the form below and we will email you with next steps.