SAP security for manufacturing
When SAP stops, the line stops. Production orders, MRP, warehouse moves and supplier deliveries all run through it, and the same systems are wired into MES, shop-floor terminals and dozens of partner interfaces. RedRays shows you where that landscape can be broken into, and who inside it already has more access than they should.
Book a demoSee the platform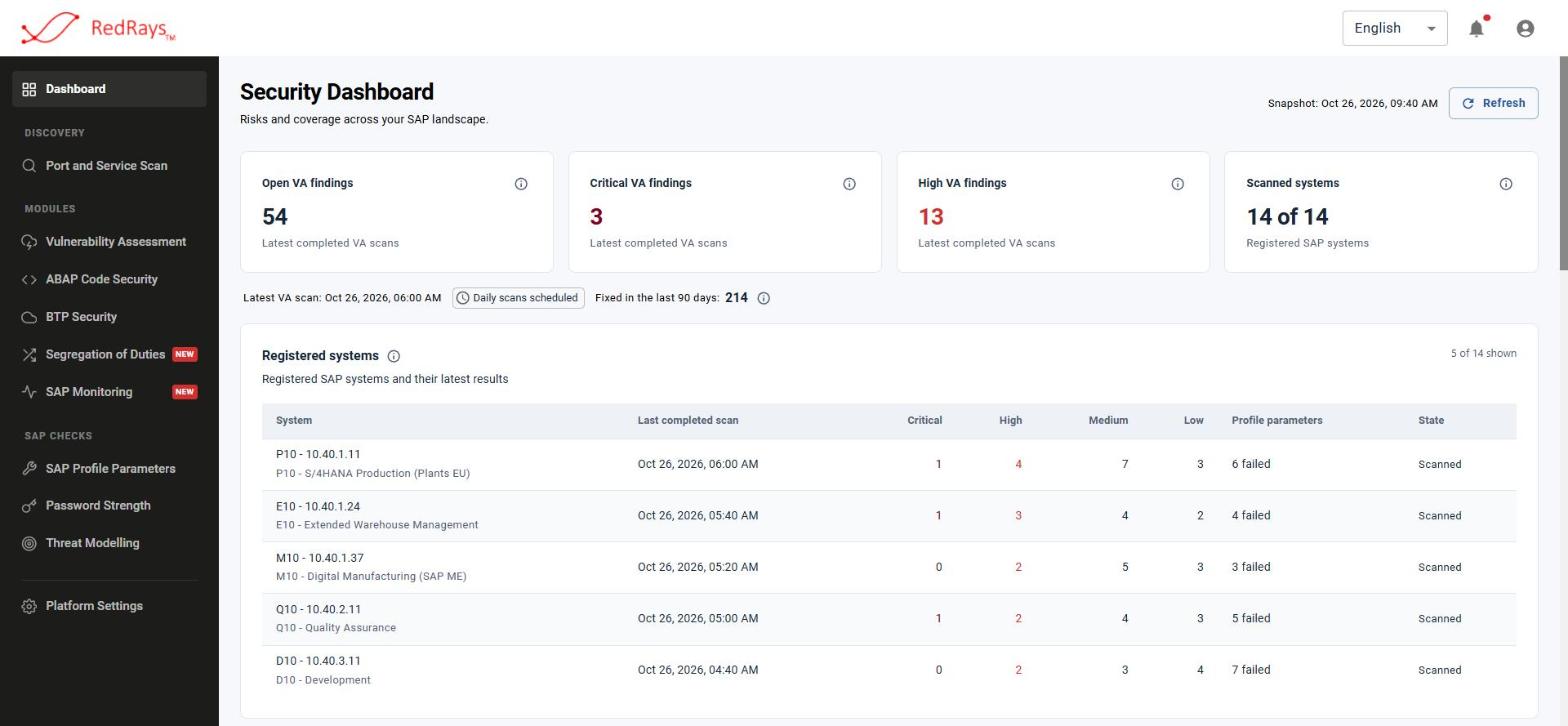
A manufacturing landscape in the RedRays dashboard. Illustrative demo data.
Where SAP risk sits in a manufacturing company
Most of the problems we find in manufacturing SAP are ordinary: an old RFC trust, a default user on a plant system, a buyer with one role too many.
Downtime is the real cost
Ransomware groups know plants cannot wait. An attacker who reaches SAP through an exposed gateway or a forgotten RFC trust can halt MRP runs and goods movements across every site at once.
Plants connect to everything
SAP Digital Manufacturing, EWM, MES gateways, EDI with suppliers. Each connection is a way in, and most were set up to work, not to be safe.
Access grows with every plant
Plant controllers, buyers and maintenance planners collect roles over the years. The result is people who can create a vendor, order from it and post the invoice.
How RedRays covers manufacturing SAP
One platform for the checks your team would otherwise run by hand, plus specialists who test it the way attackers do.
Vulnerability assessment across every system
Daily scans of S/4HANA, ECC, EWM and SAP DM for missing SAP Notes, weak profile parameters, default users and open services.
SAP vulnerability assessment →Threat monitoring for production clients
Incidents for SAP* logons, SAP_ALL assignments, gateway program registrations and OS commands run from SAP, in a queue your SOC can work.
Segregation of duties for procure-to-pay
Find buyers who can also maintain vendors and planners who can release their own orders. Test role changes in what-if mode before you transport them.
Threat modelling of plant interfaces
Map RFC destinations and trusted connections between plants, central systems and MES, and see which compromise spreads where.
SAP threat modelling →ABAP code security for custom logic
Scan the Z-code behind your production and warehouse processes for injection, missing authority checks and hard-coded credentials.
ABAP code scanner →Integration and BTP checks
Audit SAP BTP subaccounts and Integration Suite flows that move orders and delivery notes between you, your suppliers and your customers.
Integration Suite scanner →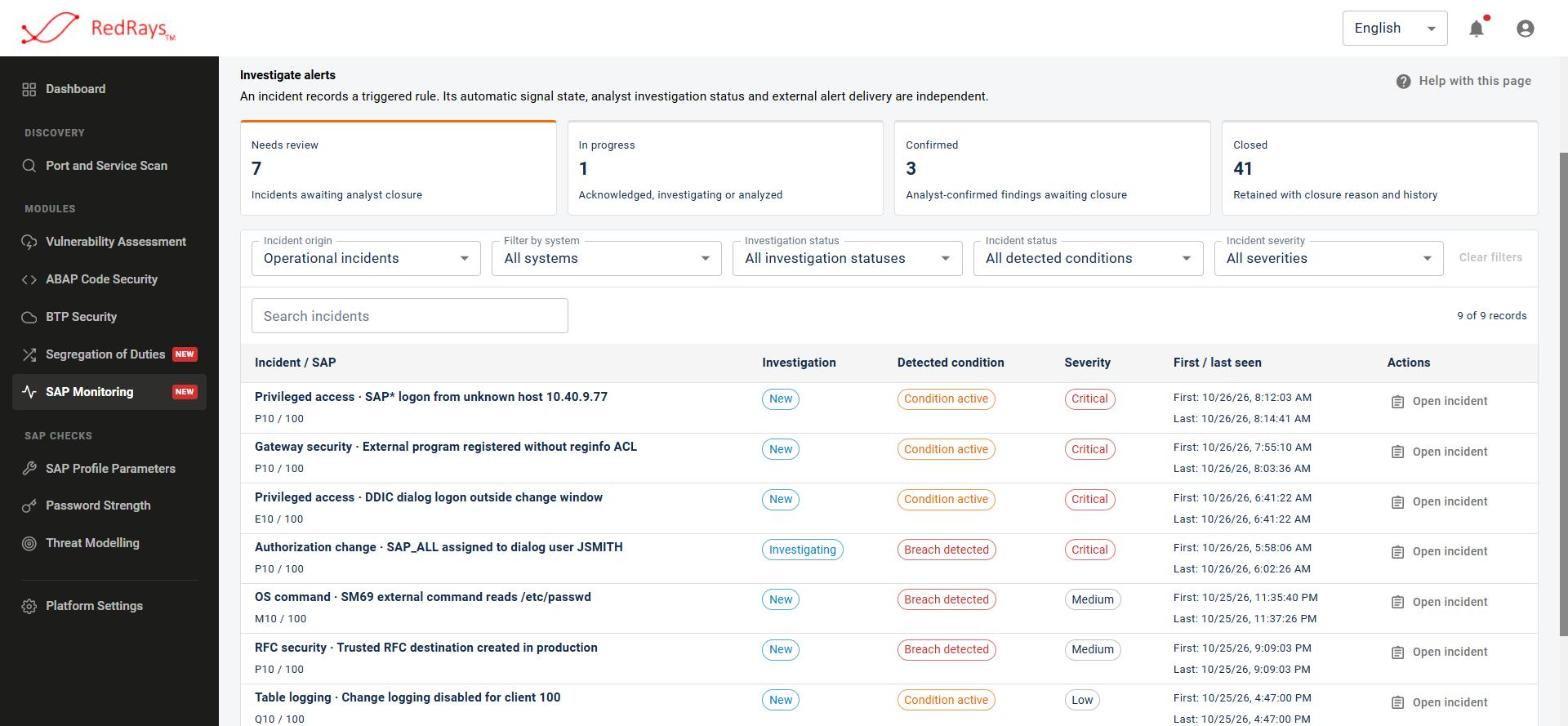
Catch the attack before the line stops
Monitoring watches the security events that matter on production clients and turns them into incidents with an owner and a status.
- Privileged logons and SAP_ALL assignments raised as incidents within minutes
- Gateway, RFC and OS command activity tracked on every production client
- Every incident keeps its investigation history and closing reason for auditors
Standards and audits
Findings are tied to the controls auditors ask about, so the scan that finds a problem also gives you the evidence that it was fixed.
Systems we cover
We assess ABAP and HANA-based systems on premises, in private cloud and on RISE with SAP, together with their integrations.
Questions we hear from manufacturers
Does scanning affect running production?
No. Assessments read configuration over RFC with a dedicated technical user and do not change anything in the system. You can also schedule scans outside shift peaks.
Our plants run separate SAP systems. Can you cover all of them?
Yes. Each plant system is registered once and the dashboard rolls results up, so you can compare plants and fix the worst first.
Do you also test our systems manually?
Yes. Our team runs SAP penetration tests that combine platform results with manual attack paths across SAP, the operating system and the network.
See your plants the way an attacker would
We will connect a test system, run the first assessment with you and walk through what we find. No slides, just your landscape.
Book a demoSAP penetration testing