SAP security for automotive OEMs and suppliers
Automotive supply chains run on SAP and on timing. Just-in-time and just-in-sequence calls, EDI with hundreds of suppliers and tight links between plants leave little room for an outage and plenty of room for an attacker to move. RedRays keeps those systems, and the access around them, in check.
Book a demoSee the platform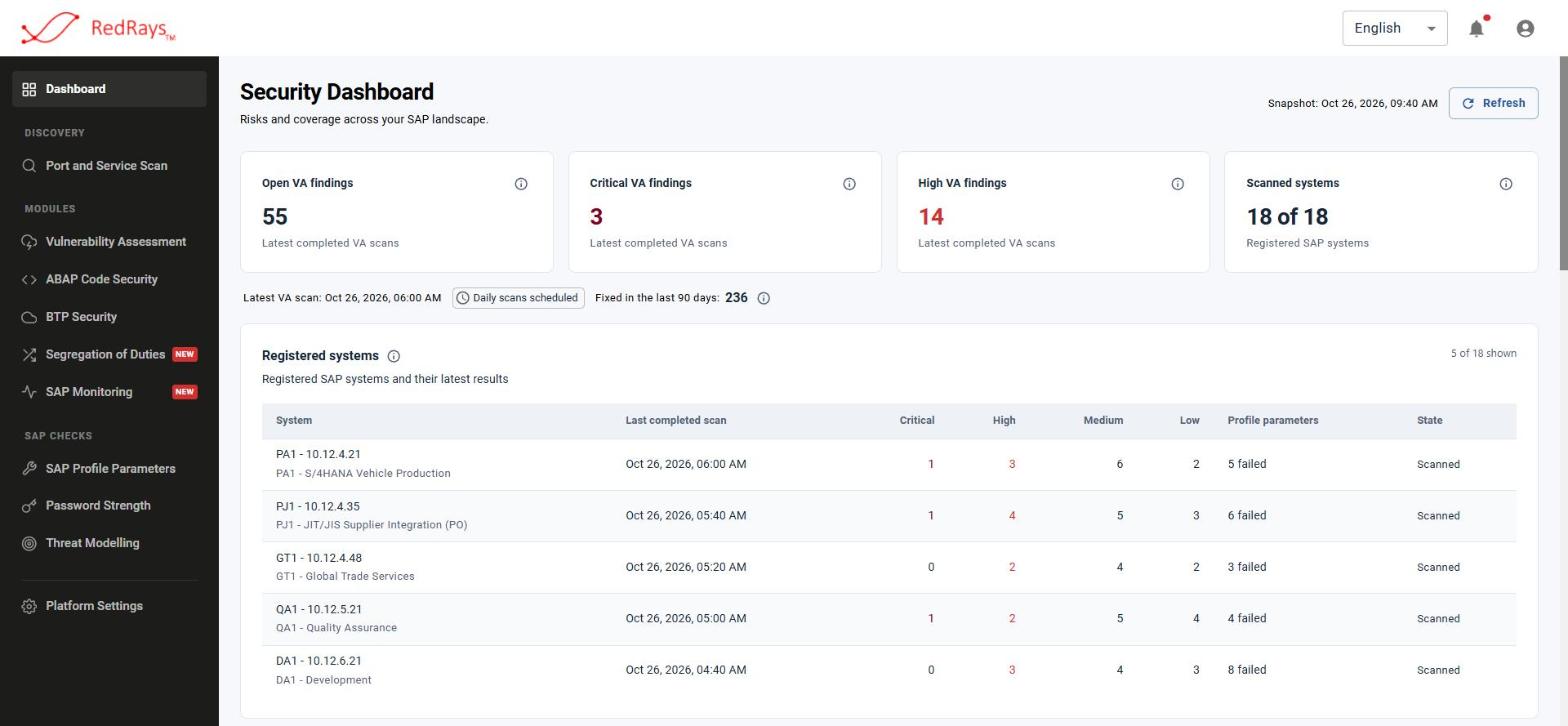
An automotive landscape in the RedRays dashboard. Illustrative demo data.
Why automotive SAP is a target
Carmakers and suppliers share data, interfaces and sometimes users. That makes the SAP landscape bigger than any one company.
A missed sequence call stops assembly
If the system that sends JIS calls goes down, the line stops within hours. That makes SAP a favourite ransomware target in automotive.
Suppliers are inside your landscape
EDI, supplier portals and shared integration flows give partners a path into SAP. A weak link at a tier-2 supplier can become your incident.
The audits never stop
TISAX assessments, OEM questionnaires and SOX controls all ask the same thing: prove who can do what in SAP and show that it is monitored.
How RedRays covers automotive SAP
Continuous checks for the systems that build and ship vehicles, and the integrations that connect you to the rest of the supply chain.
Daily vulnerability assessment
Missing SAP Notes, insecure gateway and message server settings, default passwords and exposed services across production, quality and supplier-facing systems.
SAP vulnerability assessment →Supplier integration security
Check Integration Suite and PI/PO channels, RFC destinations and the technical users that connect suppliers to your plants.
Integration Suite scanner →Threat monitoring
Incidents for privileged logons, critical authorization changes and suspicious RFC activity on production clients, ready for your SOC.
Segregation of duties
Spot users who can maintain suppliers, raise orders and approve payments, and see which roles cause the most conflicts.
ABAP code security
Scan custom code in sequencing, EDI and logistics programs before it reaches production.
ABAP code scanner →SAP penetration testing
Manual testing of the paths an attacker would take, from a supplier-facing interface to the production client.
SAP penetration testing →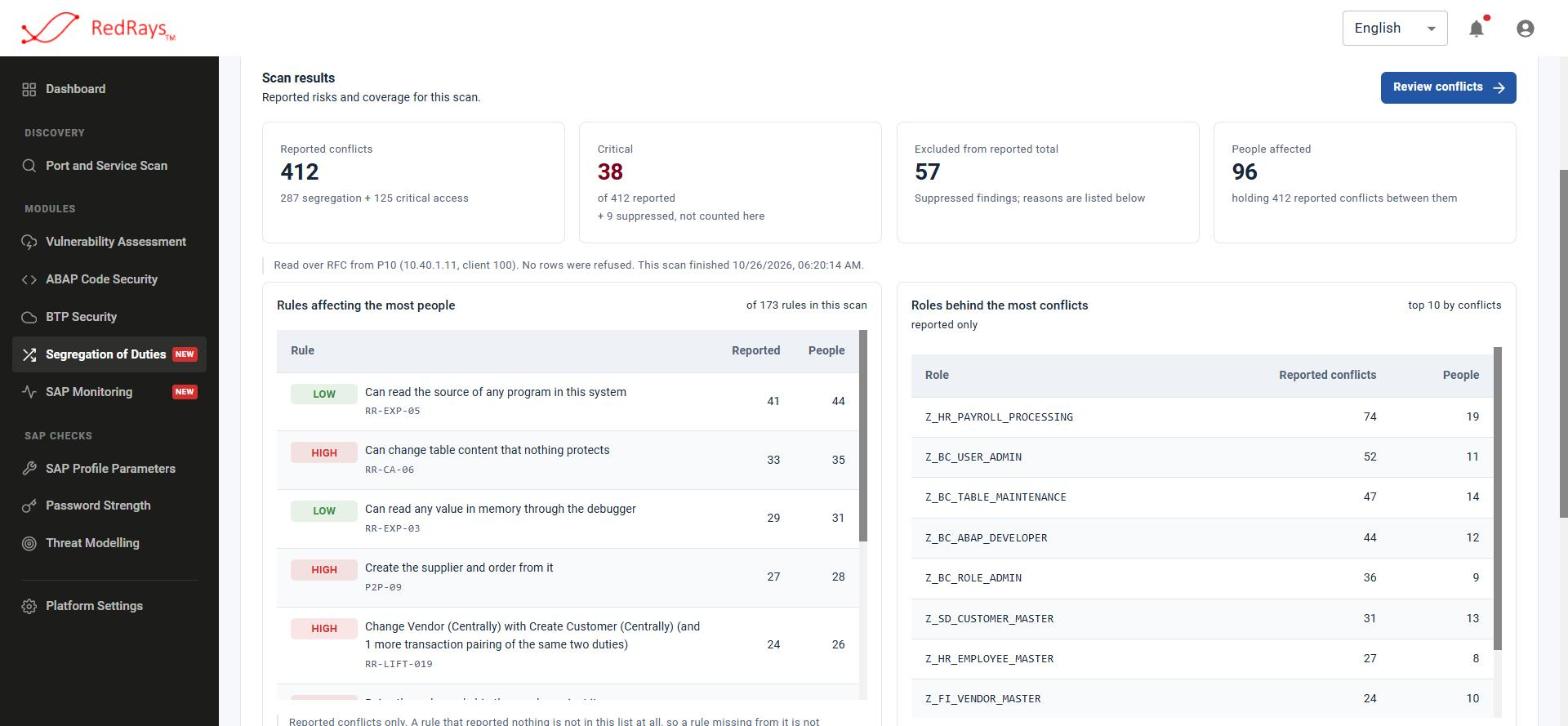
Know who can change suppliers, prices and payments
The SoD module reads users and roles straight from SAP and shows the conflicts that matter, ranked by how many people they affect.
- Rulesets for procure-to-pay, order-to-cash, HR and critical basis access
- What-if analysis shows the effect of a role change before it is transported
- Access reviews and reports you can hand to TISAX and SOX auditors
Standards and audits
RedRays does not issue TISAX labels, but its reports cover the SAP side of access management, vulnerability management and logging that assessors check.
Systems we cover
From vehicle production to global trade, we assess the ABAP and HANA systems in your landscape and the interfaces that feed them.
Questions we hear from automotive teams
Does RedRays help with TISAX?
We do not issue TISAX labels. Our reports give you evidence for the access management, vulnerability management and logging controls in your SAP systems, which is the part assessors usually ask about.
Can supplier-facing systems be monitored separately?
Yes. Group systems by environment, plant or business unit and send incidents to the team that owns them.
What do you need to get started?
A technical user and network access to the SAP hosts. After that, registering a system takes minutes and the first assessment can run the same day.
Keep the line moving and the auditors happy
Book a demo and we will run the first assessment on one of your systems together with your team.
Book a demoSAP penetration testing