SAP security for retail and consumer goods
Retail SAP landscapes move fast: promotions, price changes, store replenishment and online orders, all fed by POS and e-commerce integrations. Peak season is the worst time for an outage and the best time for fraud. RedRays keeps watch so your team can keep selling.
Book a demoSee the platform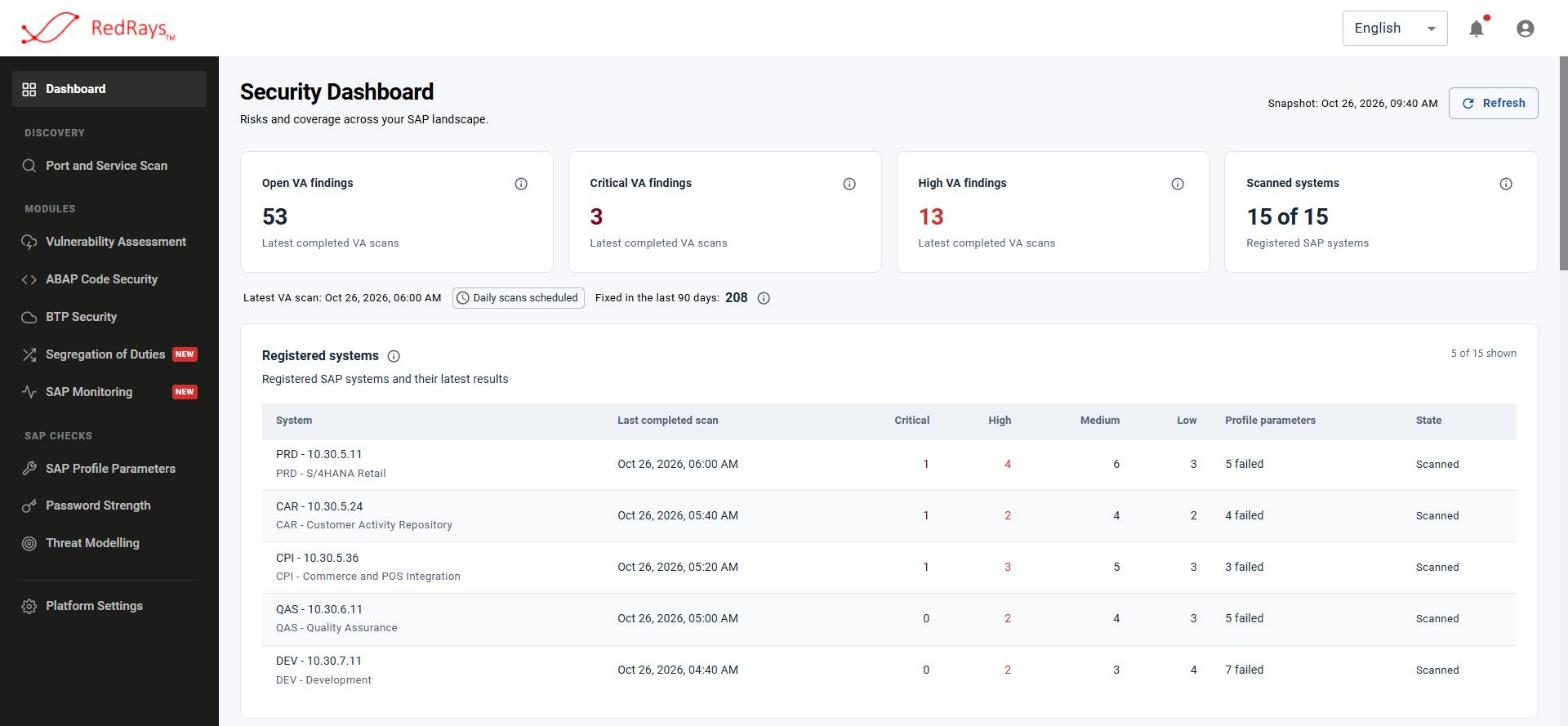
A retail landscape in the RedRays dashboard. Illustrative demo data.
Where retailers get hurt
Retail SAP risk comes from speed: many integrations, many users and constant change.
Peak season, peak risk
Attackers time ransomware for the weeks you can least afford downtime. Unpatched SAP systems are an easy way in.
Integrations everywhere
POS, webshops, marketplaces and logistics partners connect through Integration Suite and custom interfaces, each with its own credentials.
Pricing and payment fraud
Users who can change prices or vendor bank details and also post documents can commit fraud that looks like normal business.
How RedRays covers retail SAP
Coverage for the core retail system, the integrations around it and the people who use it.
Vulnerability assessment
Daily checks of S/4HANA Retail, CAR and supporting systems for missing SAP Notes, weak settings and exposed services.
SAP vulnerability assessment →Integration Suite scanner
Find insecure iFlows, credentials in plain text and over-privileged communication users in the flows that connect stores and webshops.
Integration Suite scanner →Segregation of duties
Spot users who can change prices or vendor bank details and also post the documents that use them.
Threat monitoring
Incidents for privileged logons, role changes and suspicious RFC activity, so problems surface before peak season does.
ABAP code security
Scan custom pricing, promotion and interface code for injection and missing authority checks.
ABAP code scanner →BTP and CAP extensions
Check the cloud extensions and side-by-side apps you build on SAP BTP.
CAP / BTP extension scan →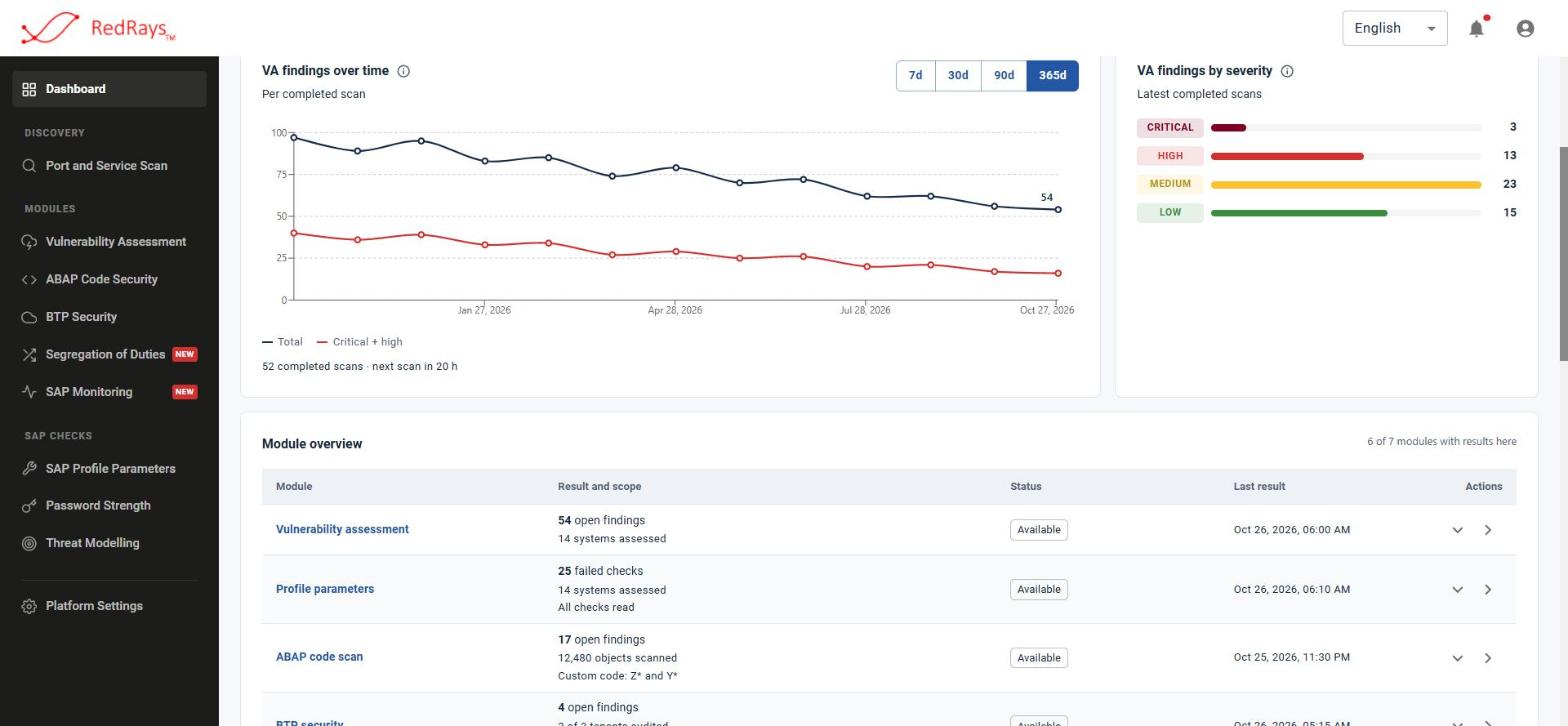
See risk go down release by release
Daily scans show whether each release, patch day and role clean-up actually reduced risk across the landscape.
- Open findings and critical findings over twelve months
- Severity breakdown for the latest scans
- Module overview of vulnerabilities, parameters, code and BTP in one place
Standards and audits
If SAP stores or processes card-related data, it is in PCI DSS scope. RedRays findings on patching, access and logging map to the requirements your assessor will look at.
Systems we cover
We assess the SAP side of retail: the core systems, the analytics layer and the integrations that POS and e-commerce use to reach SAP.
Questions we hear from retailers
Are POS systems in scope?
We assess the SAP side: the interfaces, technical users and Integration Suite flows that POS and e-commerce use to reach SAP.
Can you help us get ready for peak season?
Yes. A combined assessment and penetration test before peak season shows what to fix first and gives monitoring time to settle in.
How much effort does it take from our basis team?
Mainly creating a technical user and opening network access. After that the platform runs scheduled scans on its own.
Get through peak season without SAP surprises
Book a demo and see your SAP landscape through an attacker’s eyes.
Book a demoSAP penetration testing