SAP security for oil and gas
In oil and gas, SAP holds the maintenance plans, work orders, hydrocarbon accounting and trading data behind physical operations, and it often sits close to OT networks. RedRays helps you find the weak spots in those systems before someone uses them to reach the field.
Book a demoSee the platform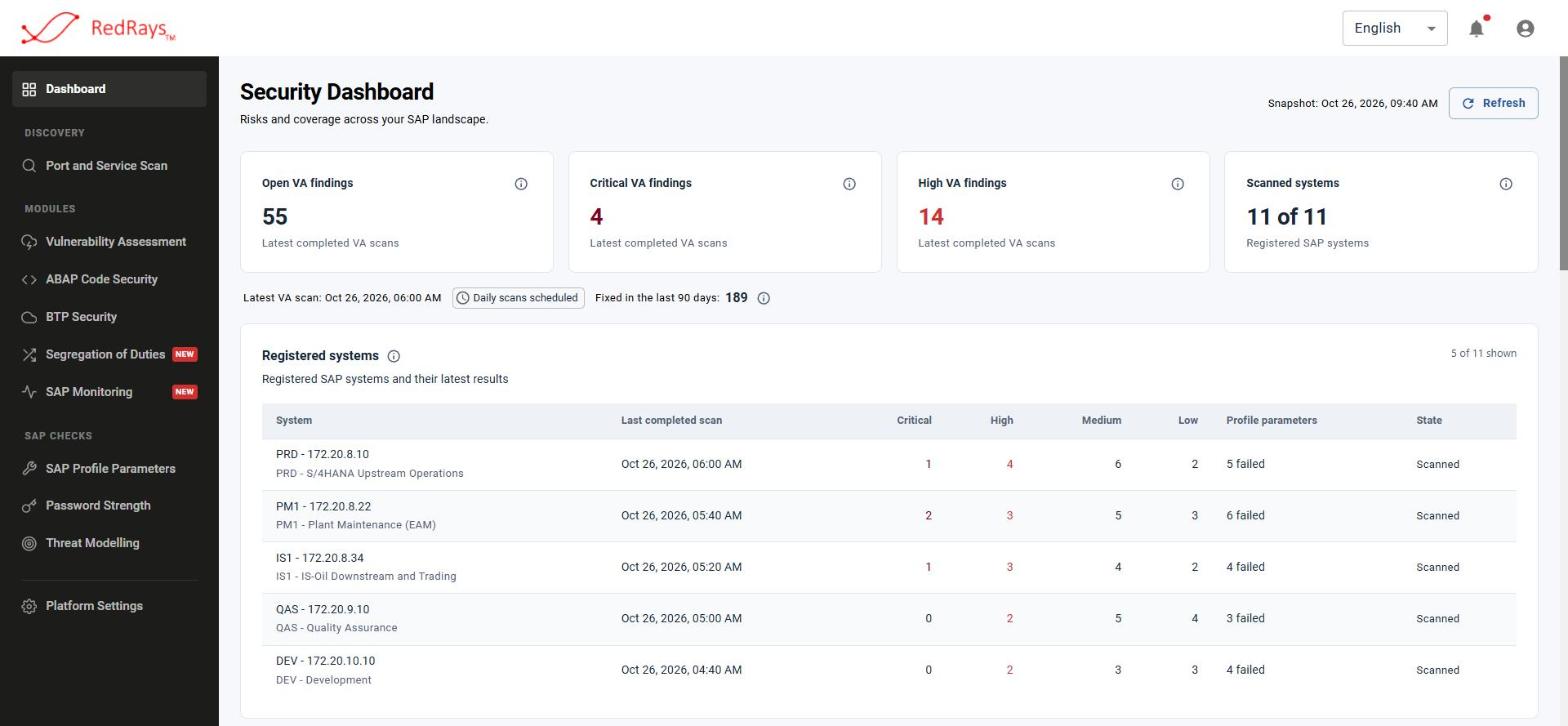
An oil and gas landscape in the RedRays dashboard. Illustrative demo data.
Where SAP risk sits in oil and gas
Remote sites, contractors and long-lived systems make SAP in energy harder to keep clean than in most industries.
IT and OT meet in SAP
Plant maintenance and EAM connect to historians and control-system gateways. A compromised SAP host can become a bridge between the two worlds.
Remote sites and shared users
Platforms, terminals and contractors often share accounts and work over limited links, so weak passwords and broad roles are common.
Regulators expect more
Pipeline operators face security directives and European energy companies fall under NIS2. SAP is part of that scope whether anyone listed it or not.
How RedRays covers oil and gas SAP
The same platform for upstream, downstream and corporate systems, with checks that reflect how energy companies actually run SAP.
Vulnerability assessment
Missing patches, weak profile parameters, insecure gateway settings and open services across S/4HANA, PM/EAM and IS-Oil systems.
SAP vulnerability assessment →Password strength checks
Find cracked and shared passwords among dialog and service users at remote sites before someone else does.
Threat modelling
See which SAP systems trust each other and where an RFC path leads from a weakly protected system to a critical one.
SAP threat modelling →Threat monitoring
Incidents for SAP* and DDIC logons, SAP_ALL assignments and OS commands executed from SAP, each with an investigation trail.
Segregation of duties
Control who can change maintenance orders, vendors and payment runs, including contractor and emergency access.
Penetration testing
Manual tests of SAP and the hosts around it, including the routes from SAP toward operational networks.
SAP penetration testing →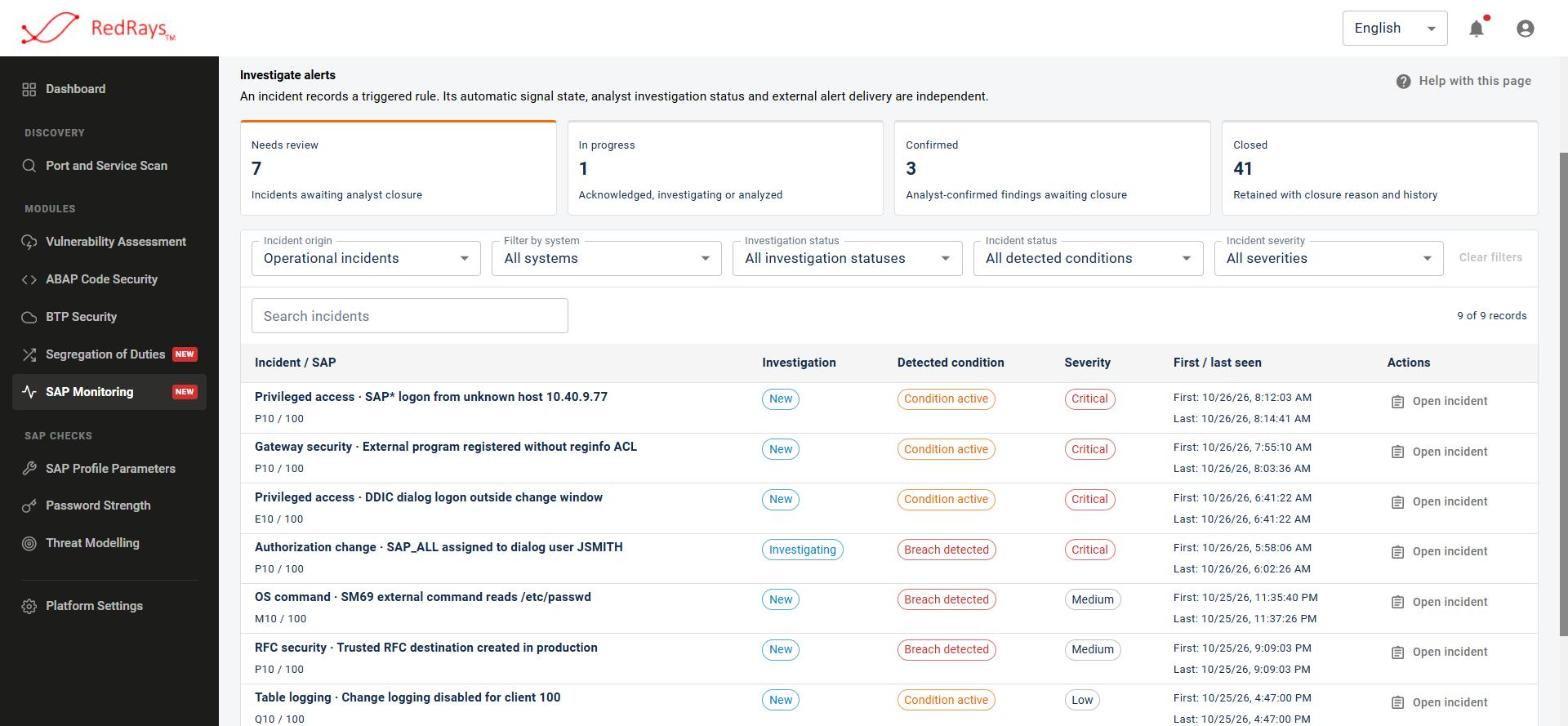
Watch privileged access at every site
Monitoring collects security events from each registered system and raises incidents your analysts can investigate and close with a reason.
- SAP* and DDIC logons flagged the moment they happen
- Critical authorization changes and OS command execution tracked on production clients
- Incident history kept for regulators and internal audit
Standards and audits
We help you show regulators and auditors that SAP is covered by the same vulnerability, access and monitoring controls as the rest of your critical infrastructure.
Systems we cover
RedRays assesses the SAP side of your operations. Threat modelling shows SAP connections that lead toward OT so your OT team can review them.
Questions we hear from energy companies
Do you connect to OT systems?
No. RedRays works with SAP systems and their hosts. Threat modelling highlights SAP connections that point toward OT, and your OT team decides what to do with them.
What if we cannot fix a finding right away?
In the SoD module you can accept a risk with a reason and an expiry date. It stays visible as accepted and comes back for review when the date passes.
Is an assessment read-only?
Yes. The platform reads configuration, users and roles over RFC with a technical user and does not change anything in the system.
Find the path before an attacker does
Book a demo and see how RedRays maps and monitors an SAP landscape like yours.
Book a demoSAP penetration testing