SAP security for pharmaceuticals and life sciences
In pharma, SAP does not just run the business. It holds batch records, quality decisions and release data that inspectors look at. Security changes have to respect validation, and security gaps can turn into compliance findings. RedRays gives you the visibility and the evidence.
Book a demoSee the platform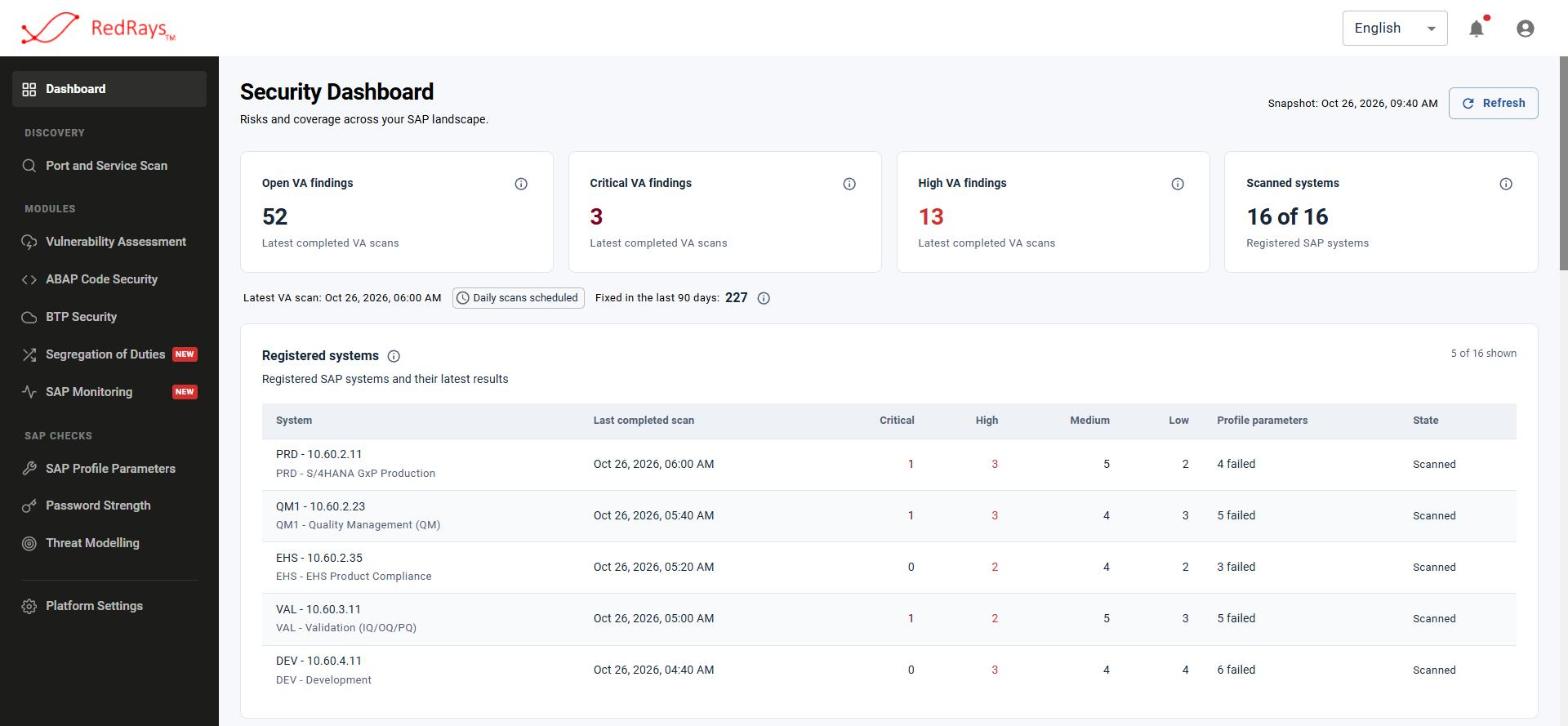
A life sciences landscape in the RedRays dashboard. Illustrative demo data.
Why pharma SAP needs its own approach
Validation, data integrity and long change cycles change how security work gets done in life sciences.
Data integrity is a security problem
If someone can change a batch status or a quality result without a trace, you have an integrity issue and a regulatory one.
Validated systems change slowly
Patching a GxP system means change control and testing. You need to know which gaps matter most so the validation window is spent on them.
Research and pricing data
Formulations, supplier specifications and pricing make pharma SAP a target for espionage as well as ransomware.
How RedRays covers pharma SAP
Read-only assessments that fit around validation, plus access analysis built for quality and release processes.
Prioritised vulnerability assessment
Missing SAP Notes and weak settings ranked by severity, so change control goes to the fixes that reduce the most risk.
SAP vulnerability assessment →Segregation of duties for quality
Find users who can record a result, approve it and release the batch, and model role changes before they reach a validated system.
Threat monitoring
Incidents for privileged logons, critical authorization changes and other security events on GxP clients, with a full investigation trail.
ABAP code security
Scan custom code in validated processes for missing authority checks and unsafe database access before it goes through validation.
ABAP code scanner →Profile parameters
Check password, logging and gateway settings against a baseline and see drift between validation and production systems.
SAP penetration testing
Manual testing planned around your validation calendar, with findings written for both IT and quality.
SAP penetration testing →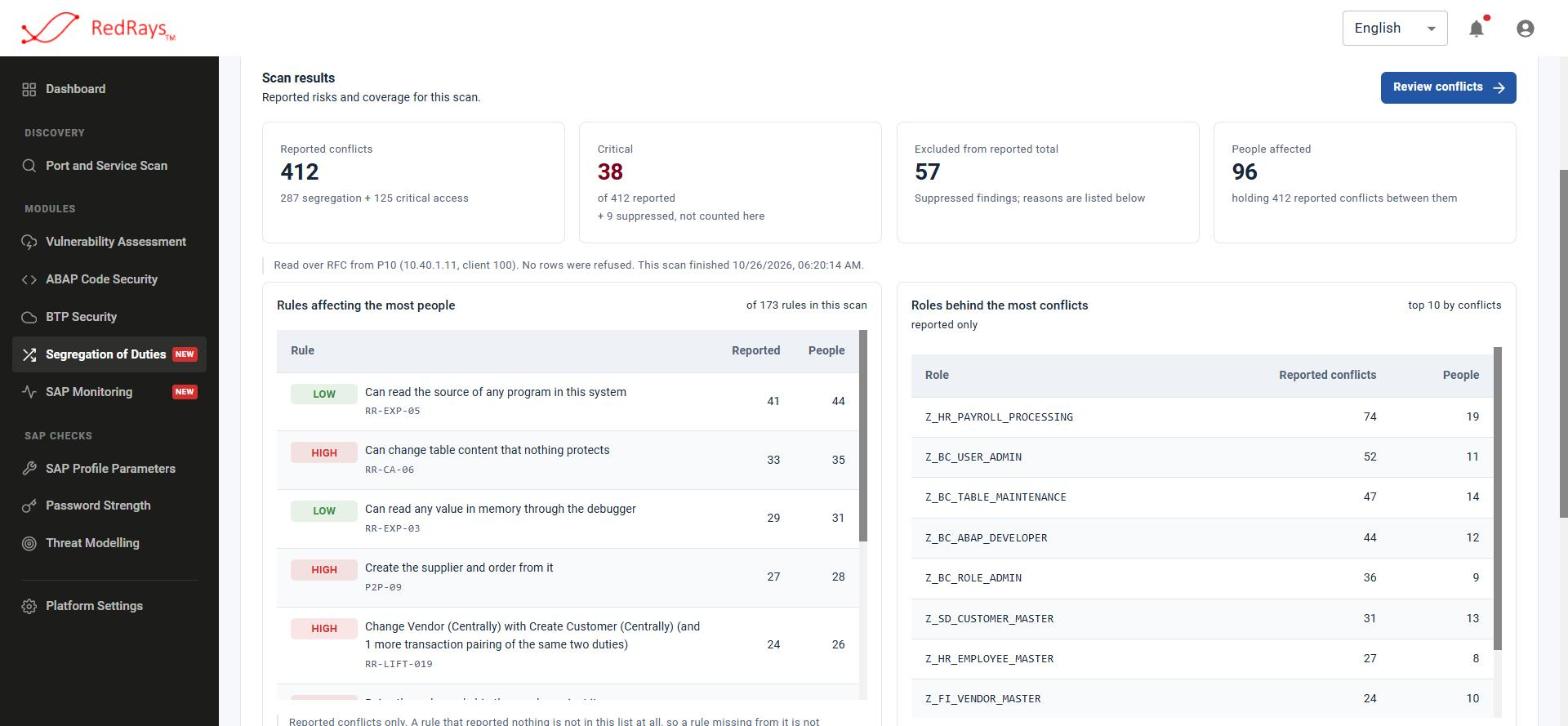
Separate who records, reviews and releases
GxP processes depend on the right people doing the right steps. RedRays shows where SAP access breaks that separation and who is affected.
- Conflicts ranked by severity and by the number of people they affect
- The roles that cause most conflicts, so you fix them once
- Risk acceptances with a reason and an expiry date for audit
Standards and audits
Use RedRays results as SAP evidence for data integrity and access control requirements in inspections and audits.
Systems we cover
We cover the SAP systems that hold manufacturing, quality and product compliance data, and the integrations around them.
Questions we hear from life sciences teams
Will scanning affect our validated state?
Assessments read configuration and do not change the system. Any fixes you decide to make still go through your normal change control.
Can we use the results in an inspection?
SoD and assessment results are available as reports you can file with your validation and audit documentation.
Do you work with our CSV or quality team?
Yes. We regularly explain findings to quality and validation teams, not just to IT security.
Keep GxP systems secure without breaking validation
Book a demo and see how an assessment fits into your change control process.
Book a demoSAP penetration testing